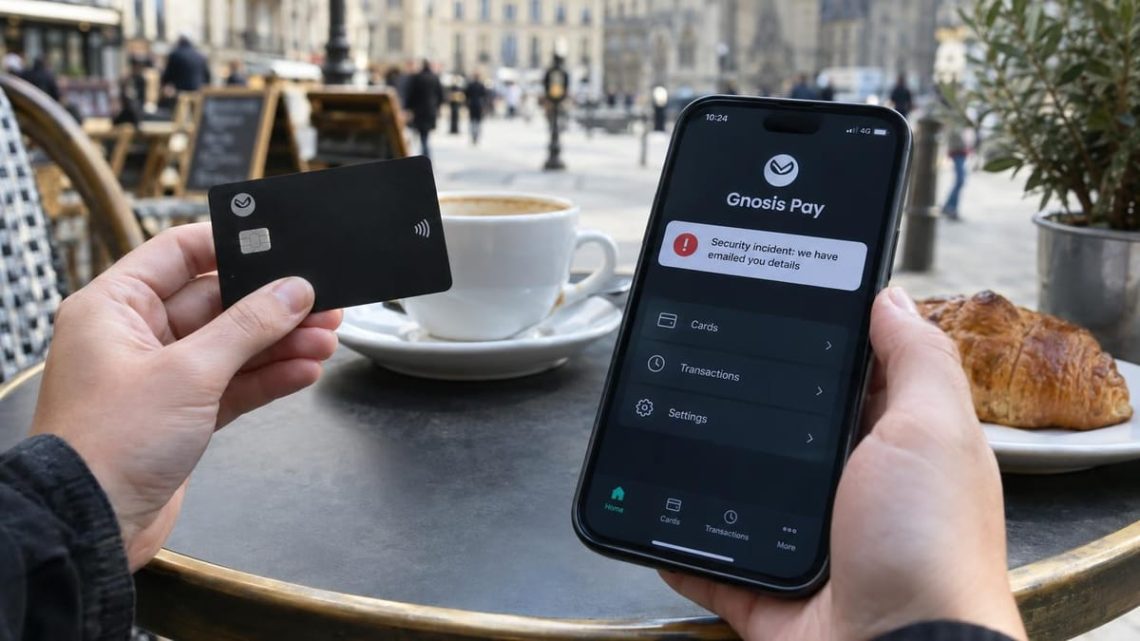

Gnosis Pay, a company that issues payment cards linked to crypto wallets, told customers on November 6 that hackers got into the system behind its own branded cards and reached customer information.[1][2] The firm says money was not touched. If you hold one of these cards, expect scam messages that use your real details, and check your inbox for the notice the company says it sent to each affected person.
What happened to Gnosis Pay
The company’s monitoring flagged unauthorized access on November 3, and Gnosis Pay says it had the intrusion contained within two hours.[1][2] It went public three days later, on Friday, November 6, in a post on X, and it also emailed customers, partners, its card issuer and data protection authorities.[1][2] One outlet that covered the incident did not state the detection date at all, so the November 3 date rests on two of the three reports.[3]

Who is affected
Only the consumer side is involved. The attackers got into the older system that runs Gnosis Pay’s own cards, sold directly to individuals. A separate business product, which lets other fintech firms and wallet apps put their own names on cards, was left untouched, the firm says.[1][2]
Gnosis Pay has not said how many customers are involved. It says each affected person got an email listing what was taken from their account.[1][2] The consumer platform was already due to be retired on December 20, so many holders are about to switch cards anyway.[1][2][3]
What data was taken
The company calls it “certain customer information” and has not published a list of data types.[2] Its own statement, as relayed by one outlet, speaks of the improper extraction of customer identification records.[3] That same report, which leans on posts from users and social media, says the data included full names, home addresses, card numbers and linked wallet addresses. Treat that list as unconfirmed until the company says so itself.[3]
There is better news on the most dangerous items. The company’s technical report, again as relayed by one outlet, says private keys, seed phrases and PINs were not exposed, and no money left user accounts.[3]
| Question | Answer |
|---|---|
| Were funds taken? | No, according to Gnosis Pay |
| Were seed phrases, keys and PINs exposed? | Company report says no |
| Which data was taken? | Not published; one report lists names, addresses, card and wallet data |
| How many customers? | Not disclosed |
| How did attackers get in? | Not disclosed |
What Gnosis Pay says it did
On X, the company wrote: “While funds were not affected, the security of personal information is just as important and we take full responsibility.”[1] It says it replaced the compromised credentials and closed the weakness. It has also stepped up fraud monitoring. Online card payments now need 3D Secure confirmation until the platform closes.[1][2]
It is also arranging specialist monitoring for any misuse of the stolen data. It has not said who the attackers are or how they got in.[1][2]
What to do now
Read the email from the company first, and keep it, because it is your record of what was taken. Then act on the advice below, which follows the company’s own guidance as reported.[1][2]
- Open the Gnosis Pay app or site only from a bookmark you saved yourself, never from a link in a message.
- Never give anyone your seed phrase, private keys, PIN or full card number. The company says it will never ask for them or ask you to move funds.
- Reject any 3D Secure approval prompt you did not trigger yourself, then look through your card transactions.
- Be careful about who learns your wallet address, especially if your name and home address were in the data. Some people may decide to move funds to a fresh address.
- Plan your next card now, and update any subscriptions before December 20.

Watch for follow-up scams
Criminals who hold a real name, address and card detail can write messages that look genuine. Expect fake alerts that say your account is suspended, refund offers tied to the breach, calls from a pretend support team, and pleas to send funds to a safe address.[2] Our guide to the Your personal data has leaked email scam shows how these lures read, and the Take Immediate Action email scam is a close cousin that pushes the same panic.
Crypto holders also face tricks that swap a wallet address at the moment of paying, so compare the first and last characters of any address before you send. We explain that in our entry on BitCoin Clipper malware.
What comes next
Watch for three updates: the number of customers hit, the list of data types, and how the attackers got in. Customers in the UK or EU also have legal rights to ask for their data, complain to a data protection authority, or seek compensation, which one report notes under UK data law.[2] The December 20 closure means the clock on moving to a new card is already running.